Current design (v5.1)
Architecture
One Bastion Core manages many Bastion Edges. Each Edge belongs to one customer, is its own cryptographic trust domain, runs on its own when cut off, and can be operated fully air-gapped.
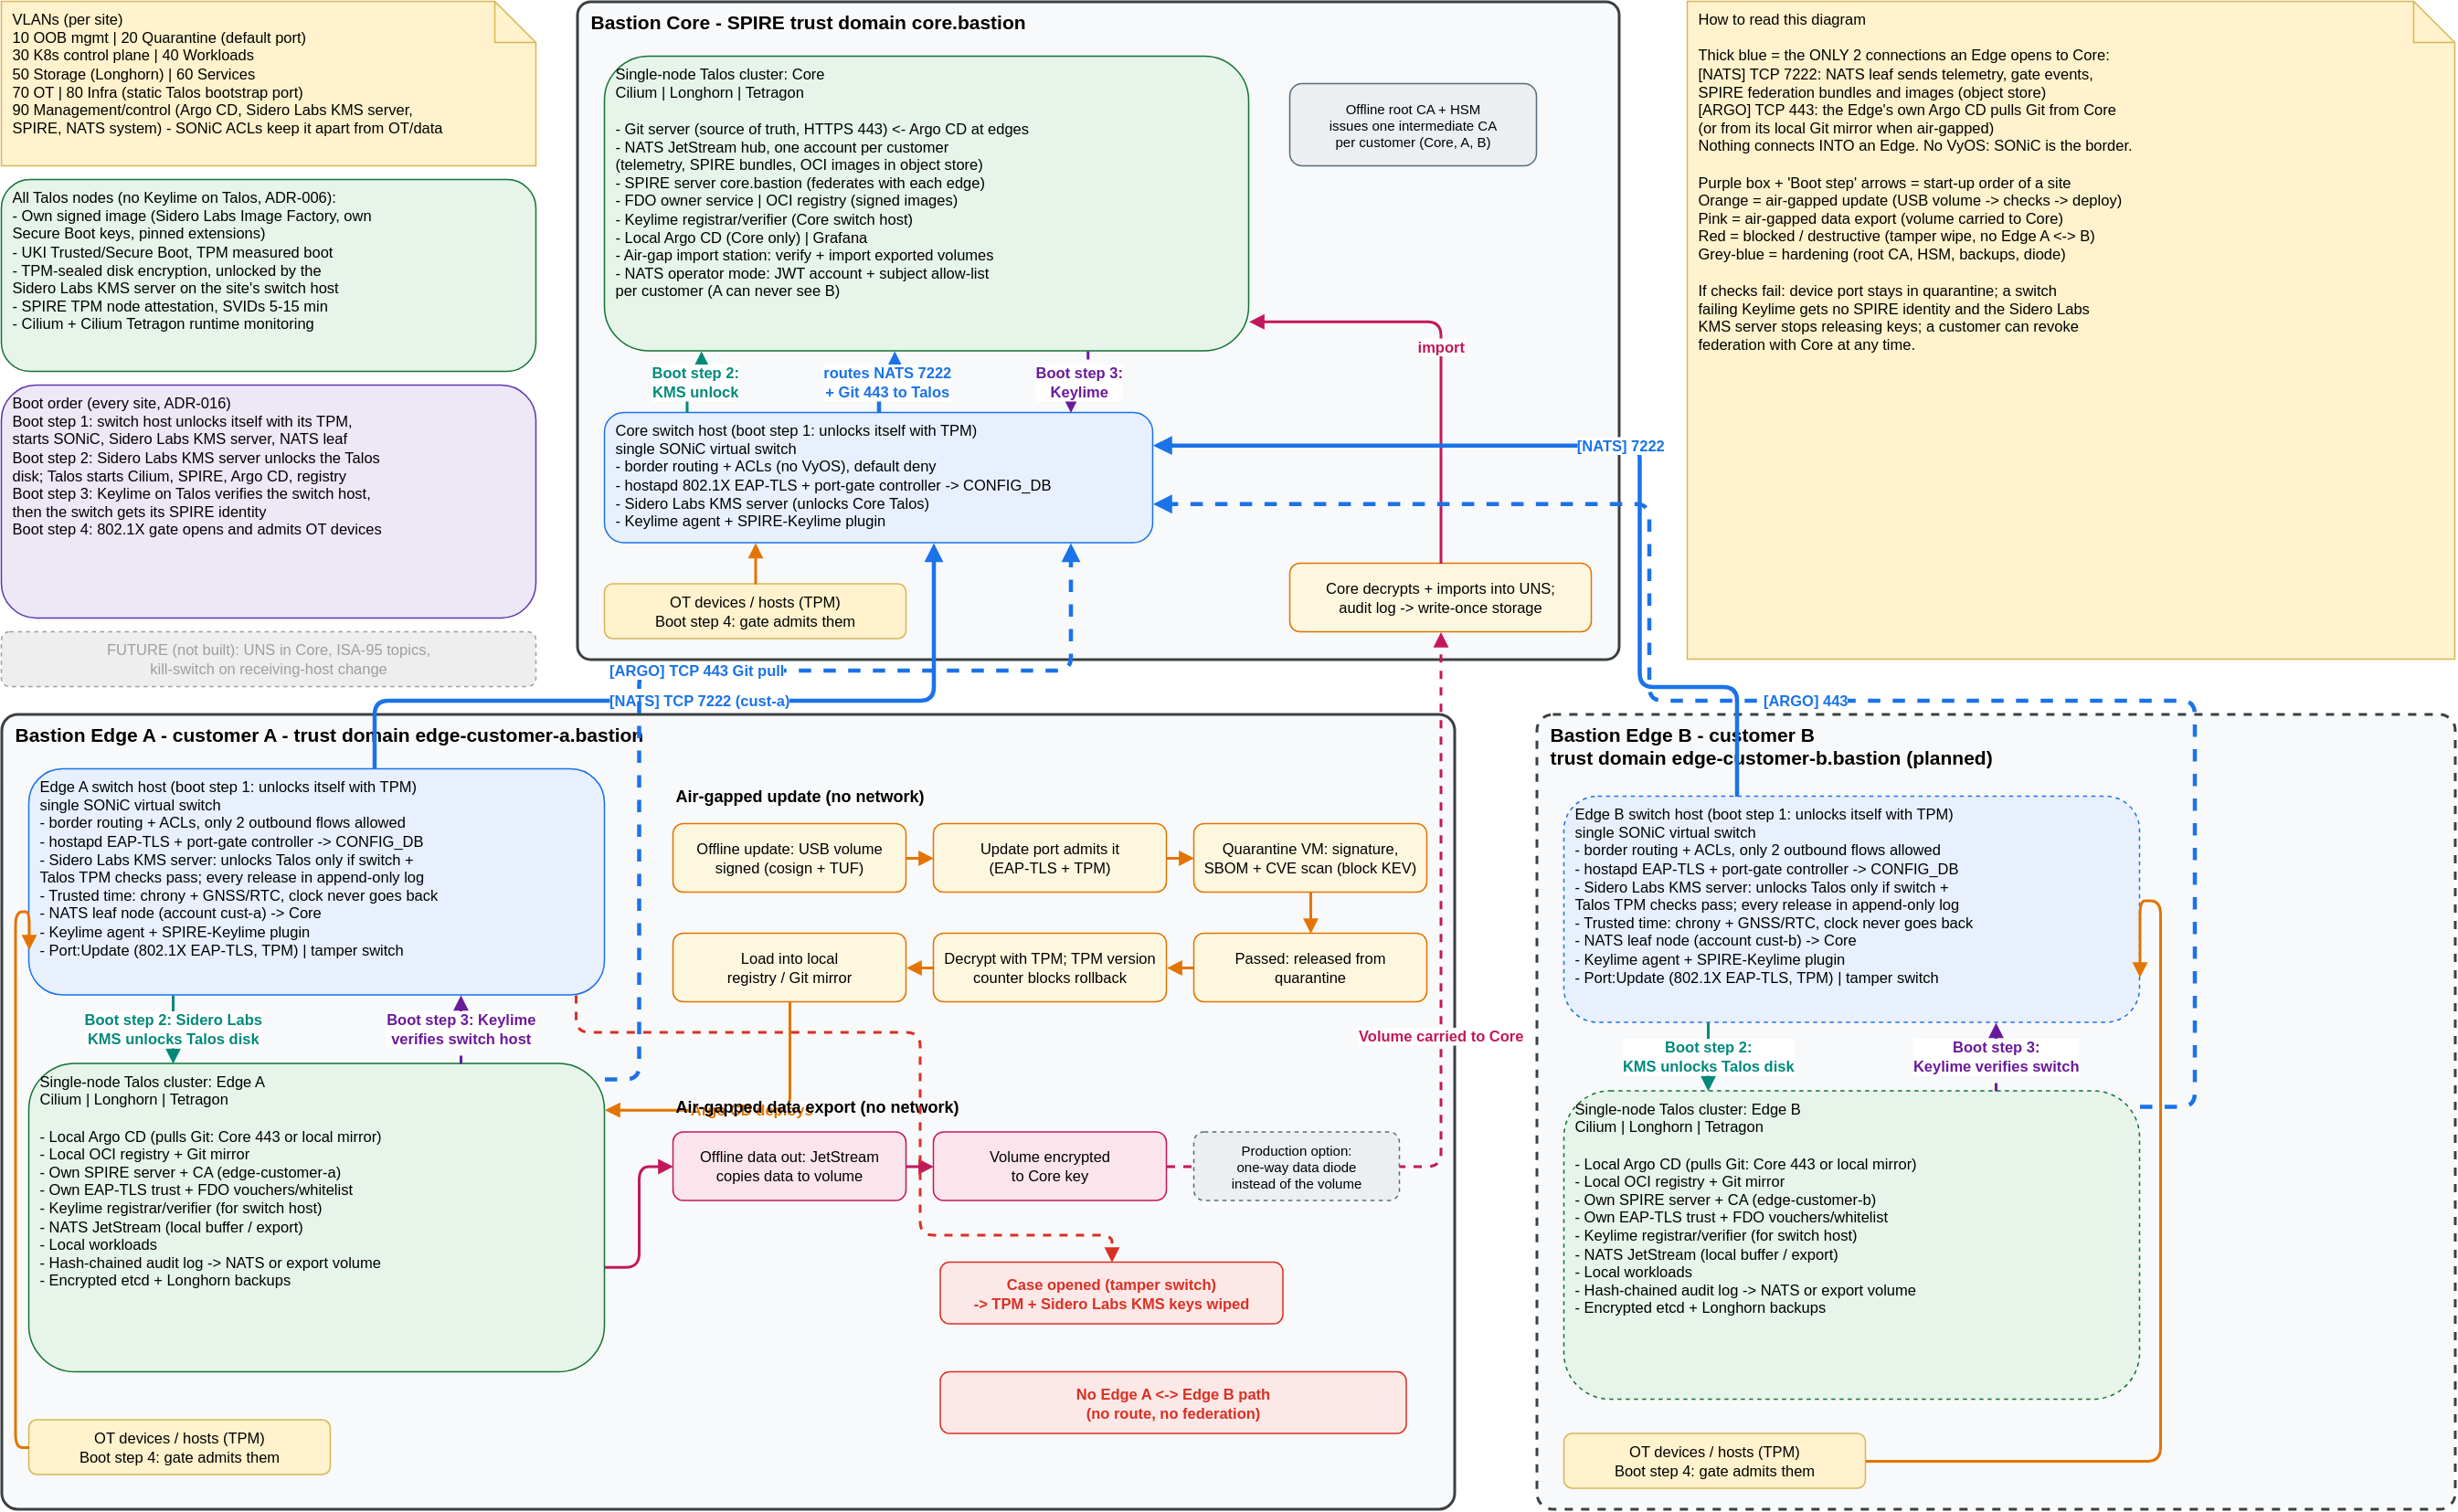
Click the diagram to open it full size. Source: docs/gcp-architecture-v5.1.png.

Design principles
- Zero trust and default deny. Every device, node and workload proves its identity with a TPM-backed credential before it gets network access or secrets.
- One trust domain per customer. Edges never trust each other. Core never holds edge keys.
- Edges are autonomous. An Edge boots, runs and updates with no connection to Core, and can be fully air-gapped.
- Minimal egress. An Edge opens only 2 outbound connections, and nothing connects into it.
- Everything is declared in Git, and signed and verified before it runs.
- Use the simplest stack that proves the point. Single-node clusters and a single switch host per site in the POC; production adds HA.